Latest from the feed

Content is curated from many trusted industry sources, including vendor advisories, security blogs, bug bounty programs, and conference organizers worldwide.

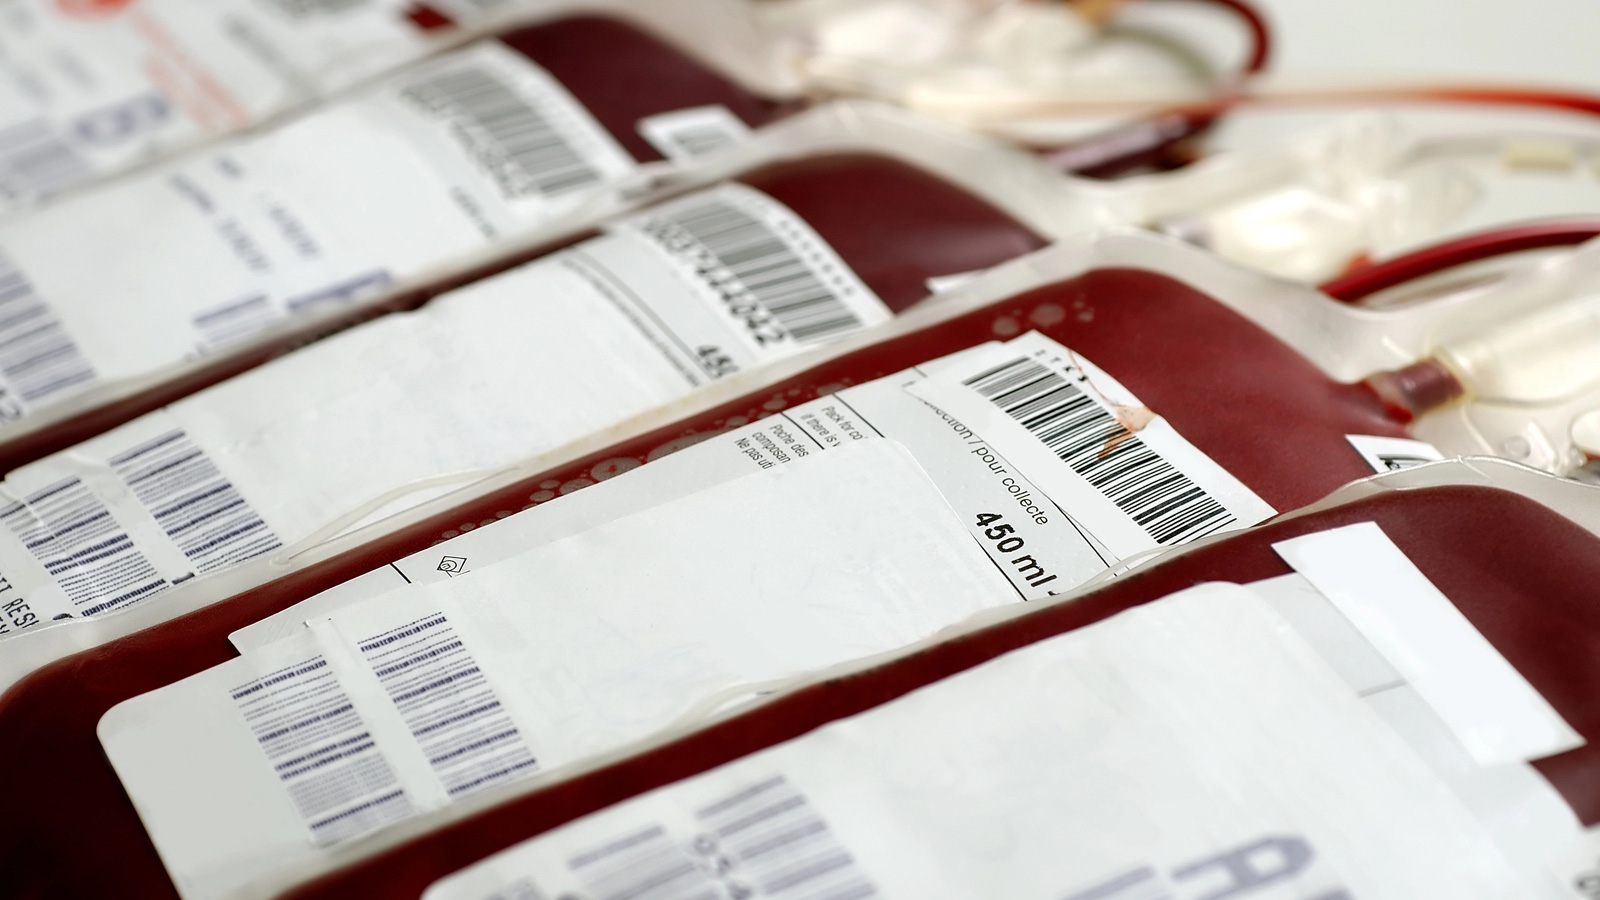
  • Refrigeration Attacks Near-Sabotage French Blood Bank

    British food wholesaler cut offline amid a broader cyberattack wave affecting European refrigeration facilities, with impacts on the food supply chain and a near-miss at France’s public blood bank. Cold storage operations saw defrosting thresholds raised and temperatures pushed to elevated levels, signaling disruption across cold-chain assets. soon.

    Source: Data Breach Today

  • NK Hackers Use Fake Interview, AI Tool to Breach Binance

    Hackers used an internal AI tool to target Binance wallet engineers after compromising an engineer via a fake job interview. They leveraged the insider tool and the engineer’s access to reach two wallet engineers and initiate a theft, draining a wallet even after withdrawals were paused, totaling billions stolen.

    Source: Data Breach Today

  • Ransomware hits blood storage fridges in France

    France's national blood service confirmed a cyberattack on a refrigeration equipment vendor disrupted cooling controls at three facilities, increasing temperatures and triggering defrost cycles. The incident jeopardizes stored blood products, prompting review of storage security, cold-chain resilience, and contingency measures to prevent spoilage.

    Source: Bleeping Computer

  • CERT-In Announces AI Security Auditing Rules in 4 Risk Areas

    India’s CERT-In has released the 107-page Artificial Intelligence Security Auditing Guidelines, outlining a framework to audit AI systems. Organizations should assess risks from autonomous AI agents, data leaks, malicious manipulation, and inadequate human oversight, with emphasis on governance, controls, and continuous monitoring.

    Source: The 420

  • US Regulator Unveils First AI Framework for Bank Examiners

    A major US banking regulator issued its first framework for examining banks’ use of artificial intelligence, directing supervisors to assess what automated systems are permitted to do and the potential harm if they fail. The OCC released the framework on November 4, 2026, outlining supervisory focus and risk considerations. It signals aware stance.

    Source: The 420

  • Crédit Mutuel Arkéa Breach: Fraudulent Transfers Reported

    Crédit Mutuel Arkéa confirms a cyberattack enabled fraudulent transactions, prompting a temporary halt on certain transfers as security teams work to contain the breach. The French bank disclosed the incident on November 4, 2026, noting attackers may have stolen as much as $133 million, underscoring ongoing incident-response. This is under review. OK

    Source: The 420

  • AI-Driven Attacks Hit Indian Banks, Fintechs: CERT-In Warns

    India's cybersecurity authorities have issued a fresh warning to banks, NBFCs, fintechs and payment service providers about AI attacks that can compromise financial systems and transfer funds at machine speed. The I4C under the Home Ministry urged institutions to bolster defenses and monitor for rapid fraud.

    Source: The 420

  • NIKKE PC Launcher Hack Delivers Remote Access, Credentials

    Goddess of Victory: NIKKE makers disclosed that hackers compromised the PC launcher scripts in a supply-chain incident, distributing malware that could exfiltrate credentials and cryptocurrency wallet data. The campaign enables credential theft, wallet access, and potential follow-on intrusions across affected environments. Patch promptly. Audit.

    Source: Bleeping Computer

  • Banned Foreign Apps Fuel ₹25 Crore Crypto Laundering in Bareilly

    A joint team from the Special Operations Group and Bhuta police detained about fifteen suspects in Khateli village, Faridpur, after a late-night raid tied to a suspected ₹25 crore hawala and cryptocurrency racket. The operation targeted an illicit network using foreign apps to enable USDT mining and laundering unaccounted funds.

    Source: The 420

  • Binance: Hackers spent months planning billion-dollar heist

    Overview of observed attacker techniques highlights three core vectors: malware-laden laptops, compromised internal tooling that undermines trusted workflows, and social-engineering ploys such as fake job interviews used to gain footholds, harvest credentials, and later expand access within organizations. It signals remote compromise. Risk to ops!!

    Source: Ars Technica Security

  • mSecure breach: reset passwords, disable passkeys, 2FA

    mSeven Software warns current and former mSecure password manager users to change their passwords, reset two-factor authentication, and remove passkeys after a cyberattack reportedly exposed an encrypted customer database. The breach underscores ongoing risks to credential storage apps and the need for proactive security hygiene.

    Source: Bleeping Computer

  • Exposing Hacking Risks in Managed Services — Cyber Friday Deep Dive

    Join us Friday, November 20, 2026 for Super Cyber Friday. The topic is Hacking Managed Services, an hour of critical thinking on risk, controls, and defense for MSPs and clients. This event post Join us on 11-20-26 for Hacking Managed Services appears on CISO Series as coverage. This session highlights security gaps and best practices for MSPs.

    Source: Ciso Series

Real-time threat intelligence1946 signals

Latest Intelligence

Refrigeration Attacks Near-Sabotage French Blood Bank
News

Refrigeration Attacks Near-Sabotage French Blood Bank

British food wholesaler cut offline amid a broader cyberattack wave affecting European refrigeration facilities, with impacts on the food supply chain and a near-miss at France’s public blood bank. Cold storage operations saw defrosting thresholds raised and temperatures pushed to elevated levels, signaling disruption across cold-chain assets. soon.
NK Hackers Use Fake Interview, AI Tool to Breach Binance
News

NK Hackers Use Fake Interview, AI Tool to Breach Binance

Hackers used an internal AI tool to target Binance wallet engineers after compromising an engineer via a fake job interview. They leveraged the insider tool and the engineer’s access to reach two wallet engineers and initiate a theft, draining a wallet even after withdrawals were paused, totaling billions stolen.

Ransomware hits blood storage fridges in France
News

Ransomware hits blood storage fridges in France

France's national blood service confirmed a cyberattack on a refrigeration equipment vendor disrupted cooling controls at three facilities, increasing temperatures and triggering defrost cycles. The incident jeopardizes stored blood products, prompting review of storage security, cold-chain resilience, and contingency measures to prevent spoilage.

CERT-In Announces AI Security Auditing Rules in 4 Risk Areas
News

CERT-In Announces AI Security Auditing Rules in 4 Risk Areas

India’s CERT-In has released the 107-page Artificial Intelligence Security Auditing Guidelines, outlining a framework to audit AI systems. Organizations should assess risks from autonomous AI agents, data leaks, malicious manipulation, and inadequate human oversight, with emphasis on governance, controls, and continuous monitoring.

US Regulator Unveils First AI Framework for Bank Examiners
News

US Regulator Unveils First AI Framework for Bank Examiners

A major US banking regulator issued its first framework for examining banks’ use of artificial intelligence, directing supervisors to assess what automated systems are permitted to do and the potential harm if they fail. The OCC released the framework on November 4, 2026, outlining supervisory focus and risk considerations. It signals aware stance.

Crédit Mutuel Arkéa Breach: Fraudulent Transfers Reported
News

Crédit Mutuel Arkéa Breach: Fraudulent Transfers Reported

Crédit Mutuel Arkéa confirms a cyberattack enabled fraudulent transactions, prompting a temporary halt on certain transfers as security teams work to contain the breach. The French bank disclosed the incident on November 4, 2026, noting attackers may have stolen as much as $133 million, underscoring ongoing incident-response. This is under review. OK

AI-Driven Attacks Hit Indian Banks, Fintechs: CERT-In Warns
News

AI-Driven Attacks Hit Indian Banks, Fintechs: CERT-In Warns

India's cybersecurity authorities have issued a fresh warning to banks, NBFCs, fintechs and payment service providers about AI attacks that can compromise financial systems and transfer funds at machine speed. The I4C under the Home Ministry urged institutions to bolster defenses and monitor for rapid fraud.

NIKKE PC Launcher Hack Delivers Remote Access, Credentials
News

NIKKE PC Launcher Hack Delivers Remote Access, Credentials

Goddess of Victory: NIKKE makers disclosed that hackers compromised the PC launcher scripts in a supply-chain incident, distributing malware that could exfiltrate credentials and cryptocurrency wallet data. The campaign enables credential theft, wallet access, and potential follow-on intrusions across affected environments. Patch promptly. Audit.

Banned Foreign Apps Fuel ₹25 Crore Crypto Laundering in Bareilly
News

Banned Foreign Apps Fuel ₹25 Crore Crypto Laundering in Bareilly

A joint team from the Special Operations Group and Bhuta police detained about fifteen suspects in Khateli village, Faridpur, after a late-night raid tied to a suspected ₹25 crore hawala and cryptocurrency racket. The operation targeted an illicit network using foreign apps to enable USDT mining and laundering unaccounted funds.

Binance: Hackers spent months planning billion-dollar heist
News

Binance: Hackers spent months planning billion-dollar heist

Overview of observed attacker techniques highlights three core vectors: malware-laden laptops, compromised internal tooling that undermines trusted workflows, and social-engineering ploys such as fake job interviews used to gain footholds, harvest credentials, and later expand access within organizations. It signals remote compromise. Risk to ops!!

mSecure breach: reset passwords, disable passkeys, 2FA
News

mSecure breach: reset passwords, disable passkeys, 2FA

mSeven Software warns current and former mSecure password manager users to change their passwords, reset two-factor authentication, and remove passkeys after a cyberattack reportedly exposed an encrypted customer database. The breach underscores ongoing risks to credential storage apps and the need for proactive security hygiene.

Exposing Hacking Risks in Managed Services — Cyber Friday Deep Dive
News

Exposing Hacking Risks in Managed Services — Cyber Friday Deep Dive

Join us Friday, November 20, 2026 for Super Cyber Friday. The topic is Hacking Managed Services, an hour of critical thinking on risk, controls, and defense for MSPs and clients. This event post Join us on 11-20-26 for Hacking Managed Services appears on CISO Series as coverage. This session highlights security gaps and best practices for MSPs.

Download Secwiser App